D-Link has warned about a zero-day vulnerability in DIR-822A routers
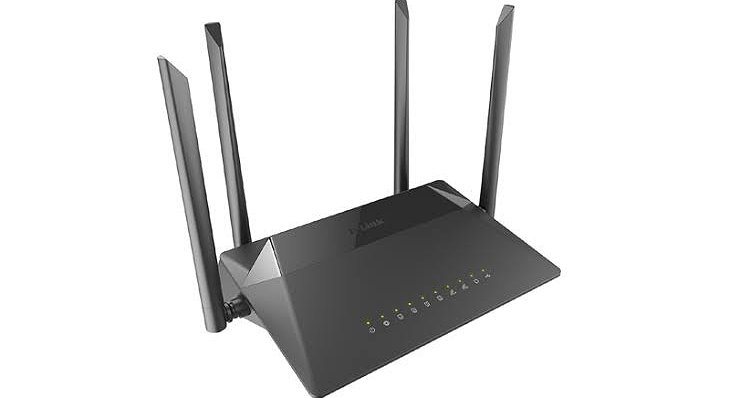
D-Link has reported a maximum-risk vulnerability CVE-2026-86296 in legacy DIR-822A routers - stack buffer overflow in the DHCP component, which can lead to remote code execution.
In parallel, D-Link is investigating the second problem, CVE-2026-86510, a critical buffer write in the L2TP message parser of the same routers, for which there is also a public PoC (Proof of Concept). It threatens devices using an L2TP/L2TPv6 connection.
Before the patches are released, D-Link recommends disabling DIR-822A direct Internet access, limiting remote management, and allowing only trusted systems to administer.
Source: dlink.com
01 October 2026

 Türkmençe
 Русский